Usually, security and infrastructure teams audit remote peripheral traffic across corporate networks. First, distributed staff mount smartcards, scanners, and licensing dongles over shared Ethernet switches. Next, unencrypted redirection streams expose raw hardware payloads to internal packet sniffers. Then, a dedicated USB Server helps. Plus, hardware boxes beat weak apps. So, we explain what transport encryption protects—and why it must pair with access controls. Thus, your network security architecture wins big. Here, smart gear stops packet sniffing panic.
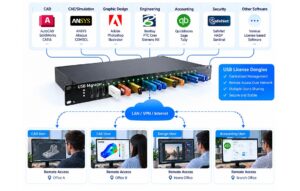 Now, stop transmitting cleartext peripheral data across shared enterprise switches. First, USB Manager provides top safety. Next, it bridges distant tools securely. Then, deep logs track every click. Plus, setup takes only five minutes. So, global IT leaders trust it. Thus, you gain absolute firm control. Finally, heavy metal stops hot dust.
Fact 1: What Gets Encrypted on the Wire: URBs and Device Payloads
Clearly, SSL/TLS USB over IP wraps raw peripheral traffic inside encrypted transport tunnels. First, client drivers encapsulate USB Request Blocks (URBs) before packets leave the workstation. Next, TLS 1.3 encrypts control transfers, bulk data payloads, and interrupt streams end-to-end. Then, smartcard PIN entries, cryptographic handshakes, and scanned document bytes become unreadable ciphertext. Plus, cryptographic integrity checks detect any mid-transit packet tampering immediately. So, packet captures on shared VLANs reveal zero readable device data. Thus, transport encryption neutralizes passive eavesdropping and man-in-the-middle interception. Indeed, network sharing brings true joy.Fact 2: Pure Software Drops Fast
Actually, cheap apps drop links fast. First, weak programs lose license data. Next, host computers freeze during tasks. Then, bad codes confuse normal staff. Plus, virtual networks lose remote ports. So, hardware servers replace cheap software. Thus, standalone gear keeps links alive. Truly, metal boxes beat weak apps.Fact 3: Supporting USB over IP
Naturally, fast networks carry digital bytes. First, physical hubs convert tool signals. Next, USB over IP moves data. Then, smart routers move packets well. Plus, distant software unpacks pure facts. So, remote computers see real tools. Thus, smart routing stops data jams. Clearly, gigabit speeds clear heavy traffic.Fact 4: What Transport Encryption Does Not Hide or Prevent
Sometimes, infrastructure teams assume an encrypted tunnel guarantees complete peripheral security. First, SSL/TLS encrypts the application payload, not outer Layer 3 and Layer 4 network headers. Next, source IPs, destination IPs, TCP port numbers, and connection timing remain visible to network monitors. Then, transport encryption never evaluates whether a connecting user actually deserves access to a port. Plus, an encrypted connection initiated by a compromised workstation still delivers full device control to an attacker. So, encryption protects data in transit, not authorization boundaries. Thus, relying on TLS alone leaves open ports vulnerable to unauthorized lateral access. Here, clear threat boundaries beat false security assumptions.Fact 5: Pairing SSL/TLS with Authentication and Port-Level Permissions
Often, true zero-trust peripheral security requires stacking identity controls onto encrypted tunnels. First, mutual TLS (mTLS) verifies both the server and client X.509 certificates before data flows. Next, administrators integrate Active Directory or LDAP to enforce granular user authentication. Then, Role-Based Access Control (RBAC) maps specific physical USB ports to authorized departmental groups. Plus, Multi-Factor Authentication (MFA) and session timeouts stop stolen credentials from hijacking idle dongles. So, every packet stays encrypted while only verified users on approved machines can mount ports. Thus, pairing SSL/TLS with authentication and permissions closes the entire security loop. Indeed, layered governance protects both the wire and the endpoint.Fact 6: Centralizing Server Room Security
Naturally, scattered keys invite bad thieves. First, cheap hubs sit openly everywhere. Next, sneaky guests steal tiny tools. Then, central vaults lock everything inside. Plus, heavy metal stops physical hits. So, firm assets stay completely secure. Thus, locked rooms protect vital cash. Truly, physical safety wins daily tests.Fact 7: Deep Audit Log Tracking
Clearly, firm bosses track hardware usage. First, basic hubs hide daily actions. Next, deep logs record every click. Then, exact login times show truths. Plus, clear reports clear all doubts. So, meeting strict compliance feels easy. Thus, passing strict audits feels fast. Here, clean logs save massive stress.Fact 8: Strict User Access Roles
Actually, normal staff make huge errors. First, open ports invite huge risks. Next, smart admins set exact roles. Then, unknown guests face locked doors. Plus, verified staff access assigned ports. So, role checks stop daily panics. Thus, firm data stays fully clean. Also, role limits protect company wealth.Fact 9: Stable Power Flow Rules
Often, sudden drops kill active tasks. First, weak voltage halts hardware chips. Next, power drops crash vital jobs. Then, smart servers deliver steady watts. Plus, dedicated supplies feed every port. So, critical dongles remain perfectly active. Hence, steady juice protects firm gear. Indeed, strong power beats cheap hubs.Fact 10: Scaling Global Branch Offices
Sometimes, growing firms expand global branches. First, tiny hubs fail daily scale. Next, ripping old wires costs cash. Then, massive racks add many ports. Plus, scalable hubs plug very fast. So, future growth feels quite easy. Thus, smart bosses plan ahead daily. Naturally, adding gear saves much stress.Fact 11: Real Time Alert Bells
Clearly, sudden drops cause big panics. First, dead links hide very well. Next, late fixes waste firm money. Then, smart servers send alert bells. Plus, red flags warn IT staff. So, remote admins fix bugs fast. Thus, instant alerts save daily cash. Here, quick news stops system crashes.Fact 12: Quick IT Deployment Steps
Usually, tricky codes confuse normal staff. First, complex software wastes IT hours. Next, real hardware plugs instantly today. Then, visual screens guide daily users. Plus, simple steps save team energy. So, total beginners deploy things fast. Thus, quick setups bring true joy. Here, easy rules beat complex codes.Fact 13: Stopping Host PC Crashes
Clearly, standard computers sleep quite often. First, sleeping hosts drop network links. Next, distant users lose active sessions. Then, dedicated hardware runs all night. Plus, industrial servers never ever sleep. So, global teams work perfectly well. Thus, standalone gear provides true freedom. Also, continuous uptime boosts firm speed.Fact 14: Reviewing Total Firm Value
Sometimes, IT budgets stay very tight. First, lost connections waste firm money. Next, dropping links kill daily output. Then, smart sharing saves huge cash. Plus, long life saves big funds. So, one big box pays off. Thus, firm wealth grows very fast. Truly, smart buys bring high value.Why Choose USB Manager?
Now, stop transmitting cleartext peripheral data across shared enterprise switches. First, USB Manager provides top safety. Next, it bridges distant tools securely. Then, deep logs track every click. Plus, setup takes only five minutes. So, global IT leaders trust it. Thus, you gain absolute firm control. Finally, heavy metal stops hot dust.
